The EU AI Act – What you need to know now
The world's first comprehensive AI regulation affects your company too. Here is everything you need to know.
What is the EU AI Act?
The EU AI Act (Regulation (EU) 2024/1689) is the world's first comprehensive regulation for artificial intelligence. It was adopted in August 2024 and has applied in full since 2 August 2026 – except for the high-risk obligations, which the Digital Omnibus (Regulation (EU) 2026/1744) postponed to December 2027 and August 2028.
The goal is to make the use of AI in the EU safe and trustworthy – without slowing down innovation. The risk-based approach distinguishes between four risk levels: minimal, limited, high and unacceptable.
Companies that develop, operate or use AI systems must meet different obligations depending on the risk level – ranging from a simple transparency requirement to a full conformity assessment.
The four risk levels of the EU AI Act
Minimal risk
Spam filters, AI in video games. No special obligations. Voluntary codes of conduct recommended.
Limited risk
Chatbots, deepfakes. Transparency obligation: users must know when they are interacting with AI.
High risk
HR tools, credit scoring, medical AI. Strict requirements: risk management system, data governance, documentation.
Affects most companies
Unacceptable risk
Social scoring, real-time biometric surveillance. Banned in the EU. No exceptions.
Which companies are affected?
Short answer: almost all. The EU AI Act applies not only to AI developers, but also to companies that use AI systems ("deployers"). This means:
- If your employees use ChatGPT, Copilot or similar tools, you are affected.
- If you use AI for HR decisions, customer analytics or process automation, you are affected.
- If you offer a SaaS product with AI components, you are affected.
The EU AI Act is particularly relevant for companies in human resources, financial services, healthcare, education and public administration.
Timeline: when do which rules apply?
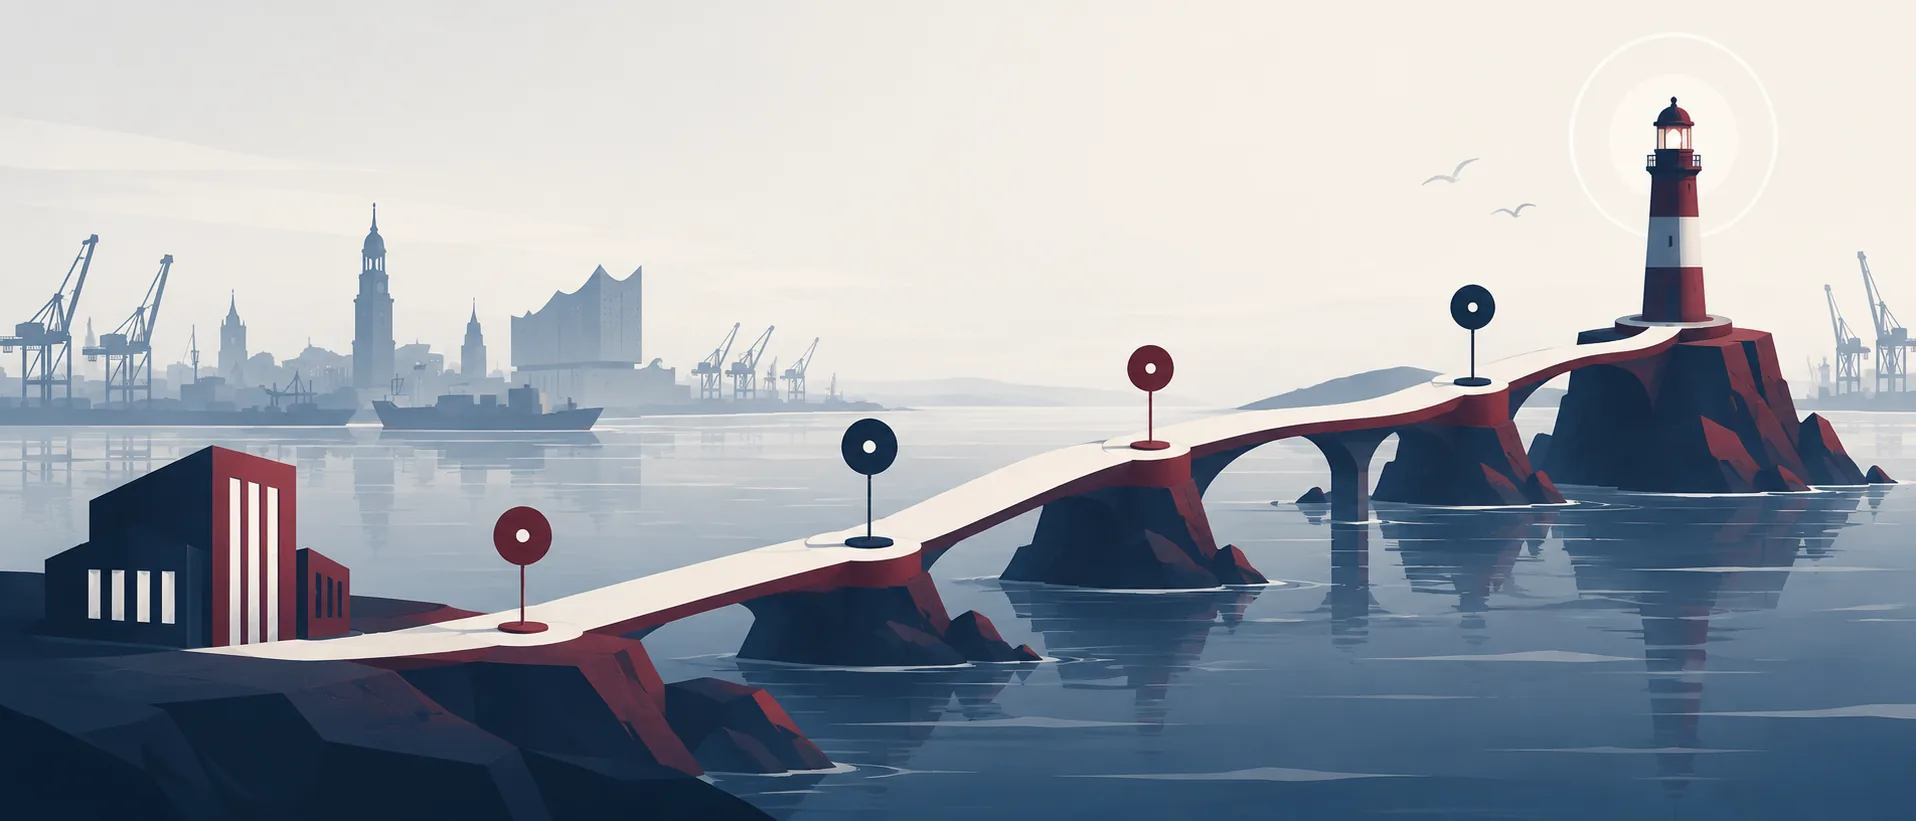
Image created with AI
Regulation enters into force
The EU AI Act was published in the Official Journal of the EU.
Bans take effect
AI systems with unacceptable risk are banned effective immediately (social scoring, etc.).
GPAI rules apply
Obligations for providers of General Purpose AI (such as GPT-4, Claude, Gemini).
General application begins
The AI Act applies as a regulation; transparency obligations (Art. 50) take effect. The high-risk obligations are still to come.
High-risk obligations apply (Annex III)
Obligations for standalone high-risk AI systems – HR tools, credit scoring and more – become mandatory. Fines of up to €15 million or 3% of global turnover.
High-risk obligations apply (Annex I)
Obligations for AI embedded in regulated products, such as medical devices, become mandatory.
How does Guardlane help with the EU AI Act?
Three steps to compliance – without external consultants.
Take inventory
Run the discovery survey. In 10 minutes, you know which AI tools are being used and where the risks are.
Implement measures
The automatically generated 30-day action plan shows what needs to be done first. Work through it sprint by sprint.
Prove & report
PDF reports for management and the works council. AI Registry as the central inventory. Everything documented and audit-ready.
The deadline is closer than your preparation time
Start your AI governance now. Self-hosted in your own infrastructure.